The Person on Your Next Teams Call May Not Be Who You Think
Microsoft Teams is preparing new deepfake detection and impersonation protections as artificial intelligence makes it easier for attackers to convincingly imitate executives, employees and trusted business partners.
For years, cybersecurity training has taught employees to be suspicious of unusual emails.
Check the sender.
Do not click unexpected links.
Be suspicious when someone suddenly asks you to transfer money, change banking information or provide a password.
Those lessons still matter.
But artificial intelligence is creating a much more difficult problem for businesses.
What happens when the person asking you to send the money appears to be your CEO — on a live video call?
Or when the voice on Microsoft Teams sounds exactly like your manager?
Microsoft is now preparing new security capabilities for Teams designed specifically to help organizations deal with this emerging threat.
Deepfakes Are Moving Into Business Communications
Deepfake technology can use artificial intelligence to create realistic-looking video, audio or images that imitate real people.
What once required sophisticated production tools is becoming easier and more accessible.
An attacker may be able to recreate someone’s voice from publicly available recordings, online videos, interviews, social media posts or corporate presentations.
Video manipulation is improving as well.
This creates a potentially powerful social engineering tool.
Instead of sending a poorly written email pretending to be the CEO, an attacker could eventually attempt to appear to be that CEO during an online meeting.
The technology does not need to be perfect.
It only needs to be convincing enough for a few minutes.
That may be all the time required to persuade an employee to:
- Approve an urgent payment
- Change banking information
- Provide confidential information
- Reset an account
- Share credentials or verification codes
- Open a sensitive document
- Add an unauthorized person to a meeting
Microsoft Teams Is Adding Deepfake Detection Support
Microsoft is preparing Teams to integrate with certified third-party deepfake detection technologies.
These security tools will be able to analyze meeting audio and video for indications that the content may have been artificially generated or manipulated.
If suspicious synthetic audio or video is detected, the detection information can be sent back into Teams so that warnings and security controls can be presented during the meeting.
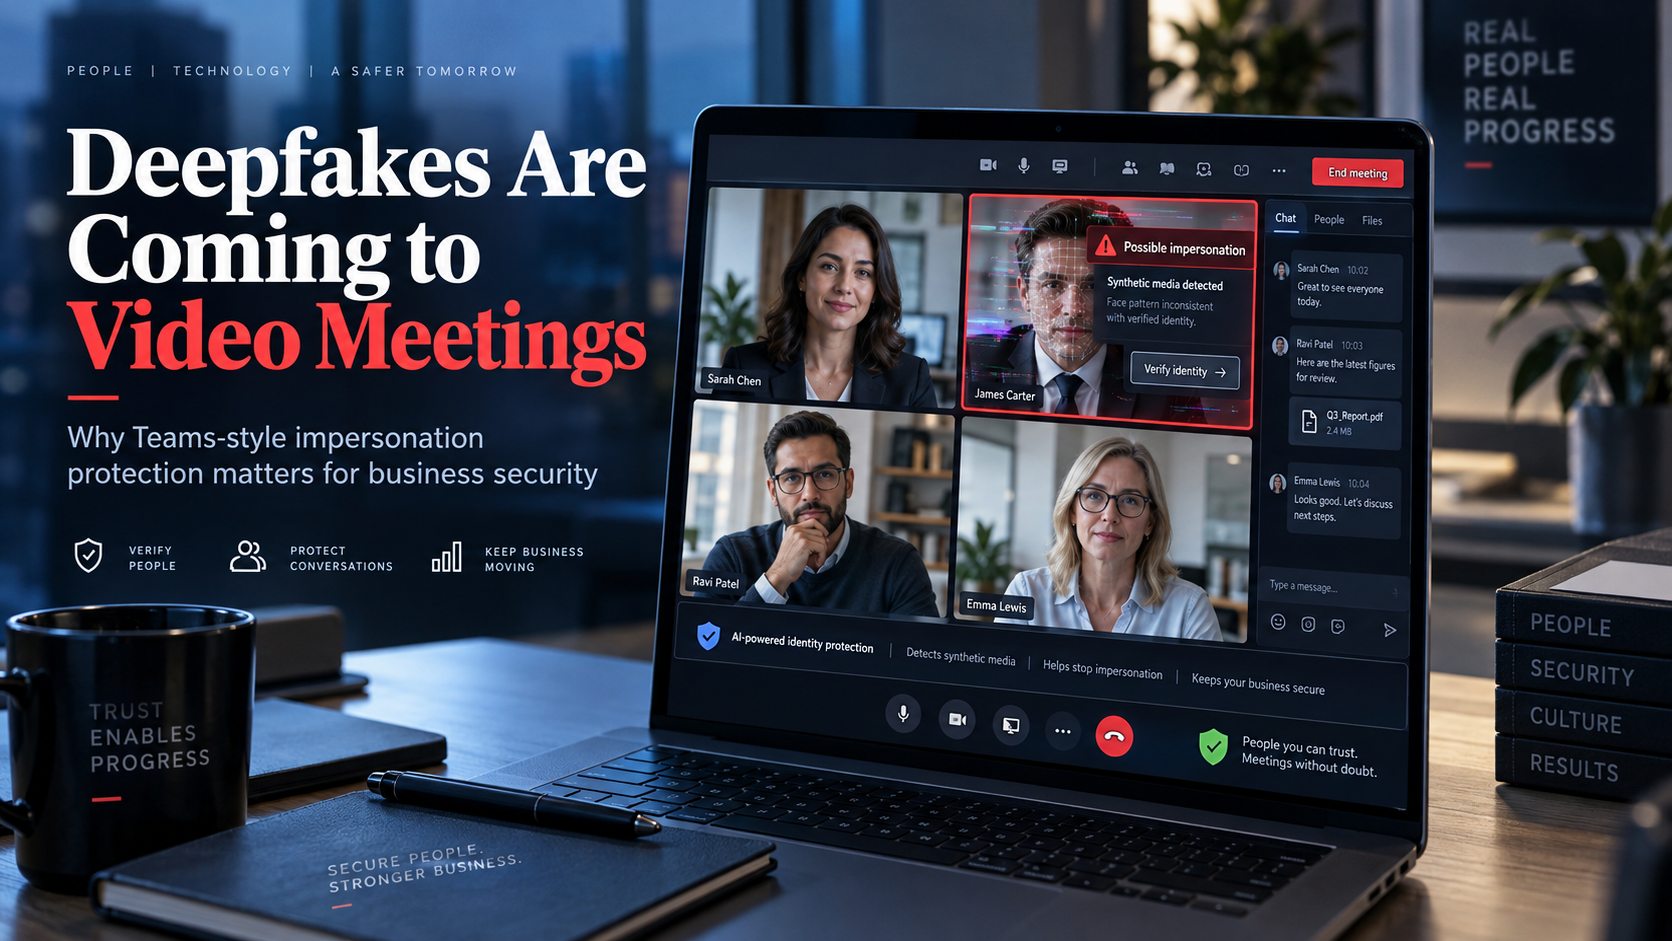
Microsoft is also developing additional impersonation protection designed to identify suspicious meeting organizers or participants.
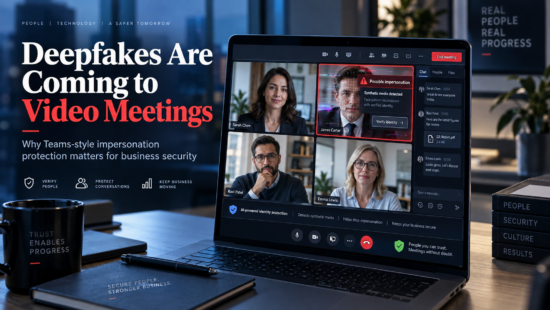
When Teams detects a possible impersonation attempt, users may see warnings or risk indicators encouraging them to verify the person’s identity before continuing.
The new capabilities are currently expected to become generally available in November 2026.
Why This Matters for Businesses
Most successful cyberattacks do not require an attacker to defeat every security system in an organization.
Sometimes they only need to convince one person.
That is why social engineering remains so effective.
Attackers create urgency, imitate authority and attempt to make employees act before they have time to question what is happening.
A realistic voice or video impersonation makes that manipulation much more convincing.
Consider a message such as:
“I’m in a meeting and need this wire transfer approved immediately. I’ll explain everything later.”
That request might already make an employee suspicious when it arrives by email.
But imagine hearing the request in the voice of the company president during what appears to be a live Teams meeting.
The psychological pressure becomes considerably stronger.
Seeing Someone Is No Longer Proof of Identity
Businesses may need to rethink one of the assumptions people naturally make about online communication.
Seeing and hearing someone is no longer absolute proof that the person is real.
Organizations already verify identities in other situations.
Banks verify customers.
IT departments verify employees before resetting passwords.
Accounting teams verify banking changes.
Businesses may now need similar verification procedures for unusual or high-risk requests made during collaboration platforms such as Microsoft Teams.
Microsoft Is Adding More Protection Across Teams
The deepfake initiative is part of a broader effort by Microsoft to improve protection inside Teams as attackers increasingly target collaboration platforms.
Teams already includes protections designed to identify suspicious external conversations and possible impersonation attempts.
When suspicious external callers or chat participants are detected, Teams can warn users and encourage them to verify the person’s identity before sharing information.
Microsoft has also introduced stronger controls around external meeting bots, allowing organizations to identify automated participants and require explicit approval before they enter meetings.
These changes reflect an important shift in cybersecurity.
Email is no longer the only place where employees need to be cautious.
Attackers are following businesses into the tools they use every day.
Technology Alone Will Not Solve the Problem
Deepfake detection will be an important security capability, but organizations should not assume that technology will identify every fraudulent interaction.
Detection systems can make mistakes.
New attacks will continue to evolve.
That means businesses still need procedures employees can follow when something feels unusual.
A simple rule can provide significant protection:
Unusual requests involving money, credentials or confidential information should be independently verified.
If someone on Teams unexpectedly asks an employee to transfer a large amount of money, the employee could verify the request using a known telephone number or another established communication channel.
Do not verify the request using contact information supplied by the person making the suspicious request.
Create a Verification Culture
One of the biggest obstacles to effective cybersecurity is the fear of appearing difficult.
An employee may worry that questioning an executive will make them look uncooperative.
That is exactly the environment social engineering attackers want.
Leadership should make it clear that employees are encouraged to verify unusual requests — even when the request appears to come from a senior executive.
A healthy security culture says:
“If something seems unusual, confirm it.”
That ten-second verification could prevent a very expensive mistake.
Five Things Organizations Can Do Now
- Require independent verification for unusual financial requests. Changes to banking information and large transfers should never rely solely on a Teams message, call or video meeting.
- Train employees about voice and video impersonation. Cybersecurity awareness programs should now include AI-generated audio, video and deepfake scenarios.
- Use strong Teams meeting controls. Review who can bypass meeting lobbies, present content and invite external participants.
- Be cautious with unexpected external participants. Verify unfamiliar guests and automated meeting bots before allowing them into sensitive discussions.
- Make verification acceptable. Employees should never be criticized for pausing an unusual request to confirm someone’s identity.
The Next Phishing Attack May Look Very Different
The classic phishing email is not disappearing.
But the definition of phishing is getting broader.
The next social engineering attempt may arrive as a text message.
It may appear inside Microsoft Teams.
It may sound like someone you know.
And increasingly, it may even look like them.
Microsoft’s decision to bring deepfake detection and additional impersonation protection into Teams demonstrates how quickly the threat landscape is changing.
Businesses should respond in the same way.
Technology can help identify suspicious behaviour.
Security controls can reduce opportunities for attackers.
But one of the most powerful protections remains surprisingly simple:
When a request is unusual, sensitive or urgent, verify the person before you trust the request.
Is Your Microsoft 365 Environment Ready for Today’s Threats?
Microsoft 365 and Teams continue to add new security capabilities, but those protections still need to be configured appropriately for your organization.
Our team can help review your Microsoft 365 and Teams security settings, external access policies, multifactor authentication, identity protections and cybersecurity awareness program to help reduce the risk of impersonation and social engineering attacks.
Because in the age of artificial intelligence, recognizing a familiar face may no longer be enough.